How to Use DKIM to Prevent Domain Spoofing
What is DKIM? DKIM (DomainKeys Identified Mail) is a cryptographic technology that senders can use to sign their messages with. DKIM allows the receiver of an email to validate that the message was originated from an approved location as set by the domain owner. When messages are not signed with DKIM, emails are more likely
1 May 2022 3 min read
This is the practical, get-it-set-up guide to DKIM – for a deeper technical explanation of how the signing and verification process actually works, see DKIM Records Explained.
What is DKIM?
DKIM (DomainKeys Identified Mail) is a cryptographic technology senders use to sign their outgoing messages. DKIM lets the receiver of an email validate that the message genuinely originated from an approved location, as set by the domain owner. Emails that aren’t signed with DKIM are more likely to be flagged as spam, or possibly not delivered at all.
How does DKIM work?
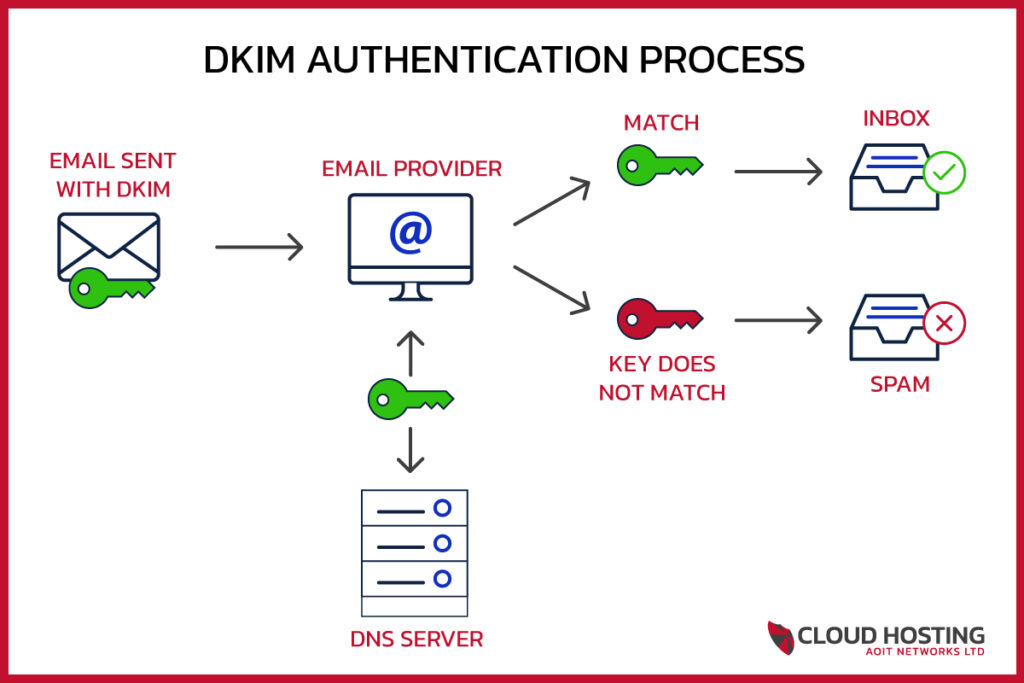
DKIM is a simple form of email authentication – its only function is to verify that the sender of an email is responsible for the domain it’s sent from. There are two steps to DKIM:
- The sender’s mail server signs the message using a private key.
- The receiving server checks the public key stored in the TXT record at
dkimselector._domainkey.domain.comto verify the signature the sender added.
How does DKIM help prevent domain spoofing?
If you implement DKIM, you’re signing your email and giving other mail servers a way to check that the message really came from your domain. This helps receiving servers detect when an email claiming to be from your domain hasn’t actually been sent or authorised by you – reducing the chance a spoofed message reaches an inbox unflagged.
Why is DKIM important?
DKIM is important because it’s one of the main ways mail servers verify a sender’s identity. Without it correctly implemented, many email providers will block your email, keeping your messages from reaching their intended recipient. That might not sound significant if it’s only a small percentage of messages, but for a business relying on email delivery, it adds up to real consequences.
How can I test DKIM?
There are a variety of DKIM testing tools available online. A DKIM analyser or checker will help you confirm you’ve published your DKIM record correctly. It’s strongly recommended you test any changes to your SPF or DKIM records before relying on them.
Our personal favourite is MXToolbox.
What doesn’t DKIM do?
DKIM gives senders a way to sign their messages so inbox providers know they’re responsible for the content and domain it’s sent from – but there are a few things it doesn’t do:
- DKIM doesn’t tell inbox providers how to handle the message. Unlike DMARC, DKIM alone doesn’t specify what should happen if a message fails or passes verification.
- DKIM doesn’t vouch for the sender’s intent. Even if a message passes DKIM verification, whoever sent it could still be a bad actor sending malicious email from a domain they legitimately control.
- DKIM doesn’t stop messages being re-sent. If a malicious email is opened and forwarded by a recipient, it can still reach and affect subsequent recipients.
What is the difference between DKIM and SPF, and do I need both?
SPF lets senders tell ISPs which IP addresses are allowed to send on their behalf. DKIM lets ISPs verify that the content sent is what the original sender intended.
Neither SPF nor DKIM fully secures email on its own – each is missing something the other provides. SPF doesn’t verify message content, and DKIM doesn’t verify which server sent the message. Both are needed together to be a genuinely secure email sender, and pairing them with DMARC (see What is DMARC?) tells receiving servers exactly what to do when either check fails.